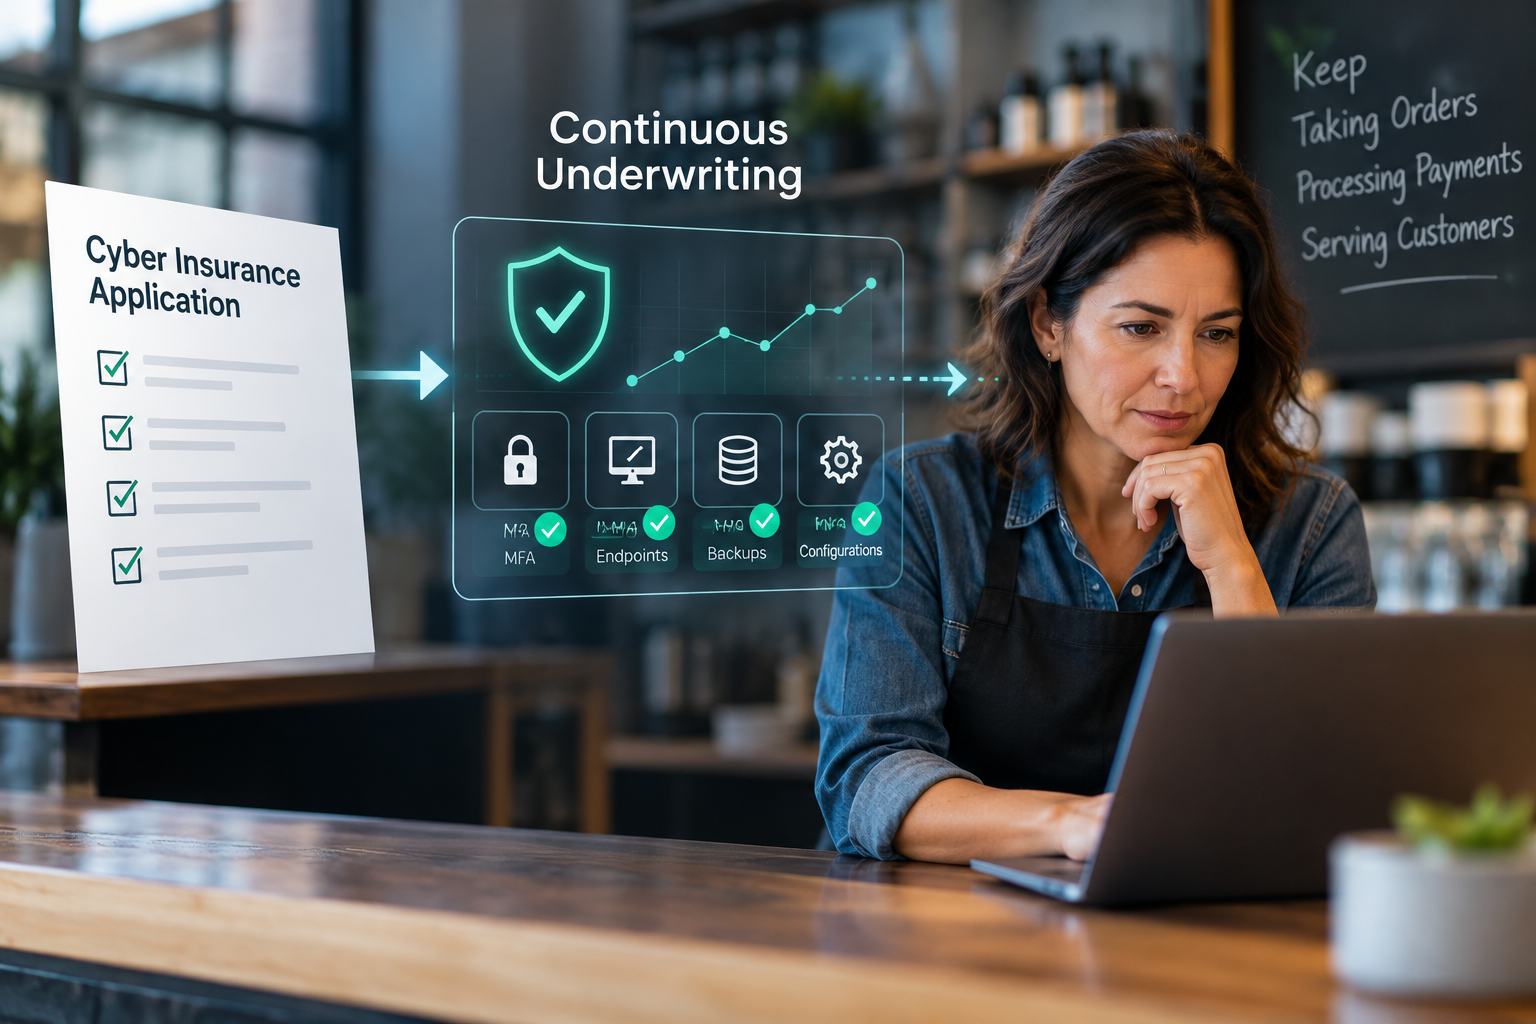
Most small businesses complete a cyber insurance application once a year and then put it away until renewal. The questions usually cover things such as multi-factor authentication, endpoint protection, backups, security awareness and incident response. Someone in the business or at the company's technology provider confirms the answers, the application is submitted and the policy is issued. The problem with this process is that the answers describe the business at a particular point in time, while the technology environment continues to change throughout the year.
A recent Dark Reading article examines how some cyber insurers are beginning to address this problem by looking beyond annual questionnaires and using more continuous information about the organizations they insure. Daniel Woods, head of emerging risks at Coalition, discusses the limitations of point-in-time underwriting when the conditions affecting cyber risk can change considerably between renewals.
For a small-business owner, the issue is fairly practical. Your company may have required MFA everywhere it was needed when you completed the insurance application. Six months later, someone may introduce a new application that is not protected the same way. New computers may not be properly enrolled in endpoint protection, or a backup process may stop working without anyone realizing it. A technology provider may change how a service is delivered. None of these situations necessarily means the original insurance application was inaccurate. They mean the conditions supporting the original answer have changed.
This is why I think small businesses should pay attention to the movement toward continuous underwriting. The insurance industry has traditionally relied heavily on businesses describing their cybersecurity controls through applications and questionnaires. Technology is making it increasingly possible for insurers to supplement those representations with evidence about the controls themselves.
For a small business, it means you should be able to support the important answers on your cyber insurance application with reasonable evidence. If you say MFA is required, your IT provider should be able to show you where it is enforced. If you say endpoint protection covers your computers, there should be a report showing the devices that are actually protected. If you say important systems are backed up, there should be evidence that those backups are occurring and that someone has successfully restored data from them.
This is particularly important for small businesses that outsource most of their technology management. Hiring an MSP does not automatically mean every control on the insurance application is operating exactly as you assume. Your provider may manage Microsoft 365 but not a separate business application. It may install endpoint protection on company laptops but not on every server. It may manage backups without being responsible for periodically testing whether the business can actually recover from them. The only reliable way to know what is being done is to verify it.
The same principle applies to recovery. A successful backup report confirms that information was copied, but it does not necessarily establish that the business can restore its critical systems within the amount of time management expects. This becomes important during a cyber incident because the financial loss is often influenced by how long the business remains disrupted. The insurance policy can help pay covered recovery costs and business interruption losses, but it cannot make an unusable backup recoverable after the incident has already occurred.
Small-business owners should therefore treat the cyber insurance application as more than paperwork required to obtain a policy. It provides a useful list of assumptions about how the business is protected. Those assumptions can be checked when the application is completed and reviewed again when something significant changes in the company.
I recommend keeping a simple evidence file with the insurance application. For the important cybersecurity questions, record who verified the answer and retain whatever report or documentation supports it. When the business adds a major system, changes technology providers or makes another significant technology change, the relevant answers can be reviewed rather than waiting for the next insurance renewal.
This also makes the renewal process easier because the company is not starting over every year. More importantly, it gives the business a way to identify when something it previously relied upon has changed. An answer that was correct last year may no longer describe the company today, and that matters whether the insurer ever asks about it.
The movement toward continuous underwriting should reinforce something small-business owners should already want to know. The important question is not whether you were able to answer yes when you completed your cyber insurance application. It is whether the controls behind those answers continue to provide the protection and recovery capability your business is depending on.